 ByteHarbour
Share data securely, without losing control of it.
ByteHarbour provides a secure and governed data-sharing layer for moving information between systems, organisations and security domains, preserving metadata, provenance and handling controls as data moves.
What it does
System behaviour
ByteHarbour provides a secure and governed data-sharing layer for moving information between systems, organisations and security domains. It connects legacy and modern applications through modular interfaces, preserving metadata, provenance and handling controls as data moves. It can operate as a standalone exchange capability or integrate with Consilium, Harbour Guard and third-party platforms. Inside Consilium it protects documents, camera feeds and secure chat, applying classification and access control to each.
Position in the ecosystem: Espanaro reports ByteHarbour operating at DCS Level 3 for document and stream sharing, which is a capability statement rather than an independent certification. Deploy it as a standalone exchange capability, or as the governed data layer across the wider Espanaro solution set.
Three principles
The principles behind ByteHarbour
Controlled
Apply defined rules and workflows to how data is shared and consumed across boundaries.
Interoperable
Connect diverse applications, formats and organisational environments through modular adapters.
Traceable
Preserve provenance, metadata and an auditable record of information movement.
The challenge
Defence, national security and critical-infrastructure organisations need to exchange information across systems and organisational boundaries without losing control of how it is handled.
Legacy integration approaches often create isolated data silos, brittle point-to-point connections and duplication, while conventional file sharing can weaken provenance, governance and assurance.
Operational value
ByteHarbour delivers:
- Controlled data exchange
- Reduced integration friction
- Preserved provenance
- Consistent governance
- Faster partner collaboration
ByteHarbour connects existing systems without forcing organisations to replace them, providing a governed exchange layer that supports controlled sharing and moves information between applications, teams and domains through configurable interfaces and policy-aligned workflows.
Architecture
How it works
ByteHarbour works in four steps, from connect to distribute.
- 01ConnectLegacy and modern systems
- 02NormaliseConsistent data structures
- 03GovernPolicy-aligned workflows
- 04DistributeApproved interfaces and partners
Core capabilities
Four building blocks for secure, governed data exchange
Ingestion & Normalisation
Connect disparate systems and convert information into consistent, reusable structures.
Governed Data Exchange
Control how information is published, requested, transformed and distributed.
Metadata & Provenance
Preserve source, ownership, classification and handling context, aligned to ACP240 (guided by STANAG 4774 and 4778). Reported at DCS Level 3 for document and stream sharing.
Audit & Integration Services
Provide traceability and connect data flows to operational applications and workflows.
Solution in action
See ByteHarbour working
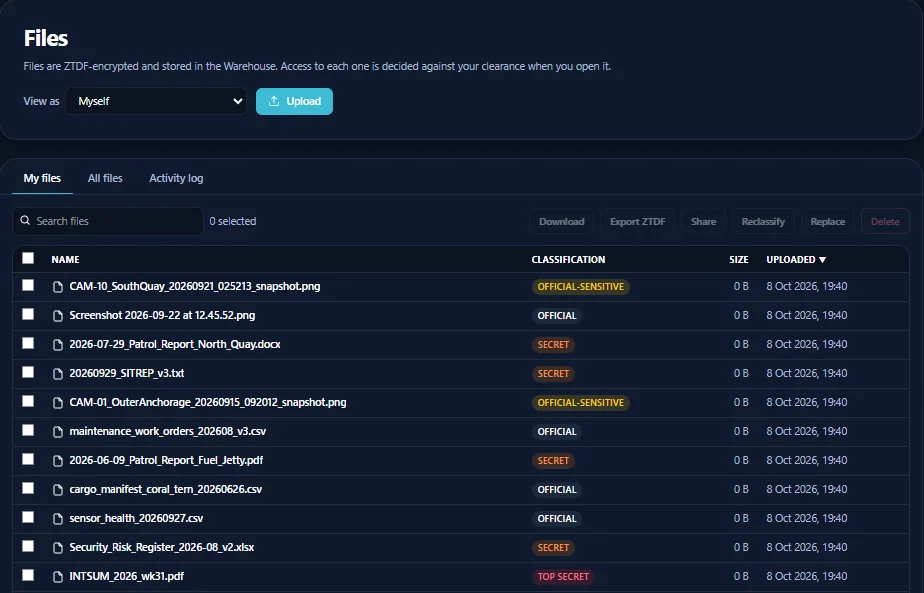
ByteHarbour protects documents, camera feeds and secure chat with classification and access control that travels with the data. These screens come from an Espanaro demonstration environment.
Files, rooms and classifications shown are illustrative demonstration data.
Use cases
Where ByteHarbour makes the difference
Cross-Organisation Data Sharing
Exchange operational information between government, industry and mission partners with defined controls.
Legacy System Integration
Connect ageing or specialist systems without requiring wholesale replacement.
Multi-Domain Information Exchange
Move data between approved environments while retaining metadata and governance.
Operational Data Fusion
Provide consistent data feeds to command, analytics and decision-support platforms.
Programme & Supply-Chain Collaboration
Enable governed information sharing across delivery partners and technical teams.
Trials & Evaluation
Test data-exchange patterns, adapters and governance models in controlled pilot environments.
Integration and deployment
Works with the systems you already run
ByteHarbour provides a governed data-exchange layer that supports controlled sharing, preserves provenance and enables information to move between applications, teams and domains through configurable interfaces and policy-aligned workflows.
| Integration area | Supported approach |
|---|---|
| Legacy & operational systems | Configurable adapters for existing databases, applications, sensors and specialist platforms. |
| Application interfaces | APIs and structured data formats including JSON and XML. |
| Message & event distribution | Event-driven and message-based patterns including MQTT and DDS. |
| Security & data controls | Integration with identity, policy and access-control services, including Harbour Guard where required. |
| Command & analytics platforms | Data consumed by Consilium, Cognisight, Pulse Sentinel or third-party systems. |
Delivered with Espanaro
Governed data sharing, built in the UK
Supported by Espanaro capability
The engineering teams behind ByteHarbour also support its integration, deployment and operation.
How to engage
- 1Discovery
Understand the data-sharing problem, environment and existing systems and interfaces.
- 2Data-Sharing Workshop
Shape adapters, governance and deployment options around your mission and constraints.
- 3Pilot
Evaluate ByteHarbour in a controlled deployment ahead of wider operational rollout.
Solution datasheet
Download the ByteHarbour Datasheet
A concise technical overview of ByteHarbour: capabilities, use cases, integration and deployment. Fill in your details and the datasheet unlocks immediately.
- Technical capability summary
- Operational use cases and deployment context
- Integration and ecosystem overview
- PDF, free to download
Discuss ByteHarbour
Share operational data securely, consistently and with control.
Speak to Espanaro about a ByteHarbour discovery, data-sharing workshop or pilot deployment.